The Hard Drive That Came Back to Haunt a Business
A company upgraded its IT infrastructure, replacing aging laptops and servers with newer equipment. Confident that the old devices were “cleaned,” the organization sent them to a local recycler and moved on with business as usual, a decision that ended in a data breach from retired hardware nobody saw coming.
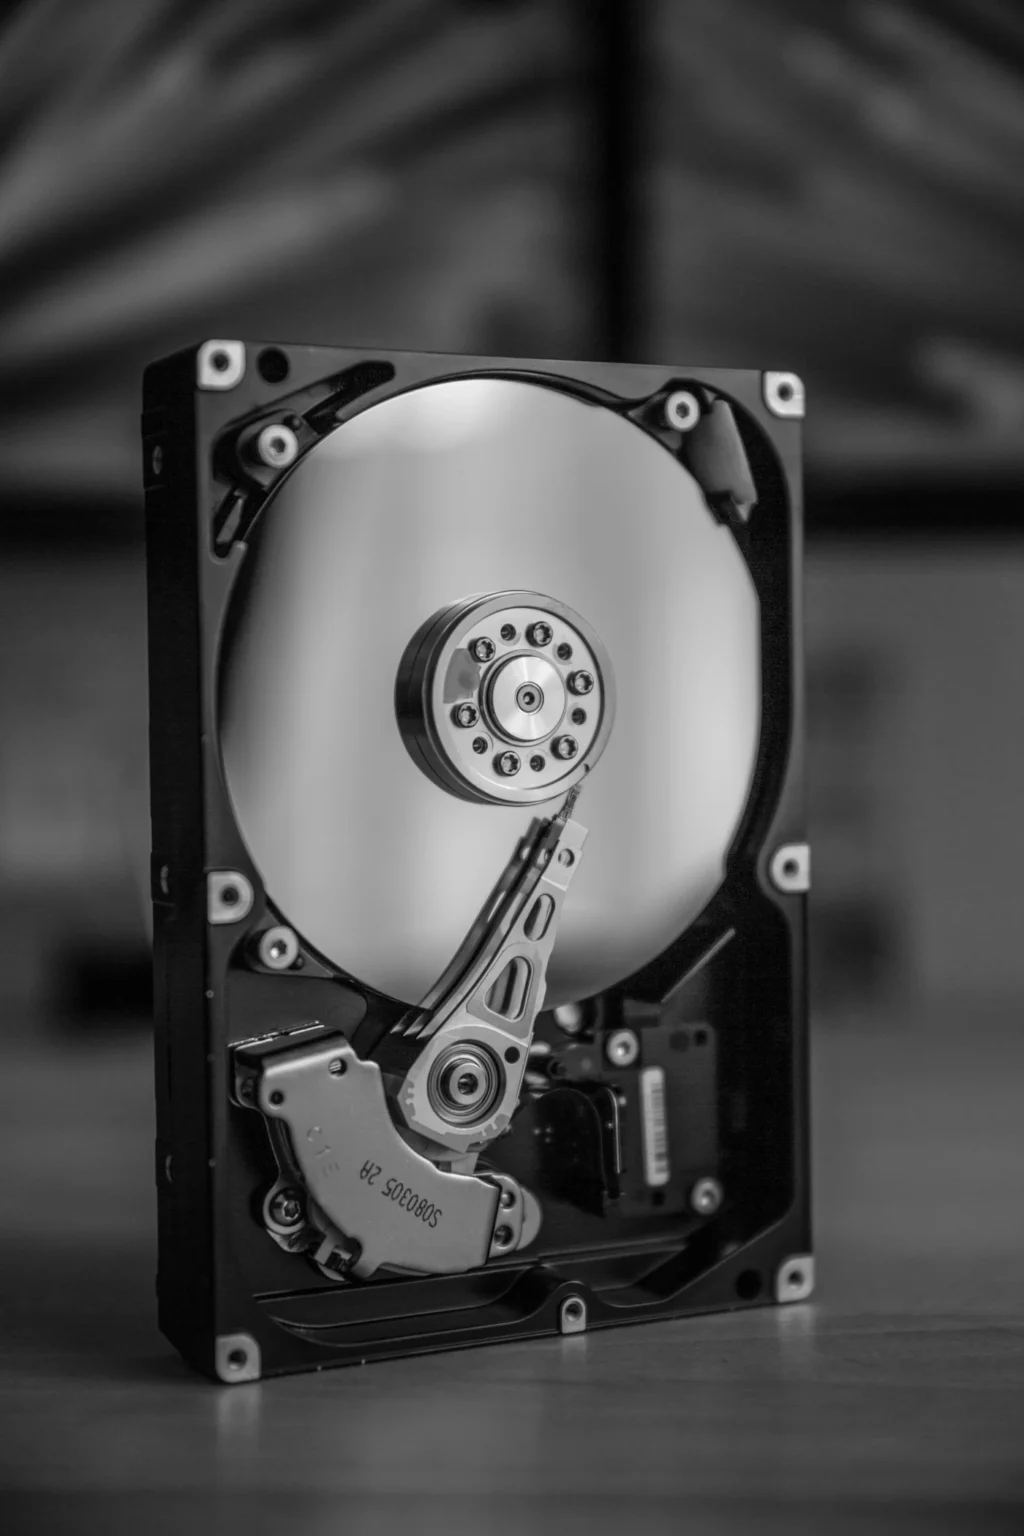
Several months later, one of those hard drives resurfaced on the secondary market. During testing, someone recovered sensitive customer information, employee records, and internal financial documents from the drive. Data the organization believed it had securely erased was still accessible.
The consequences extended far beyond replacing a few pieces of hardware. The business faced an internal investigation, regulatory scrutiny, expensive remediation efforts, legal expenses, and reputational damage that took years to rebuild.
Unfortunately, this scenario is far from uncommon.
When organizations think about cybersecurity, they often focus on active threats, phishing attacks, ransomware, malware, or network intrusions. Yet one of the most overlooked breach vectors is hardware that has already left the building.
Retired servers, laptops, storage arrays, desktops, and external drives can still contain valuable information long after they’ve left production. Without proper IT asset disposition (ITAD), those devices can become an unexpected source of data exposure.
A successful cybersecurity strategy doesn’t end when equipment reaches the end of its lifecycle. It extends all the way through secure retirement and final disposition.
The Problem: Retirement Doesn’t Mean Data Is Gone
Many organizations assume that once they stop using hardware, it no longer presents a security concern. That’s a dangerous misconception, and one of the most common paths to a data breach from retired hardware.
Deleting files, formatting a drive, or resetting a device to factory settings doesn’t necessarily remove the underlying data. Depending on the storage media and the method used, information may still be recoverable long after a device has been retired.
This creates significant risk when equipment is:
- Sold without proper sanitization
- Donated to another organization
- Sent to uncertified recyclers
- Left in unsecured storage
- Disposed of without documented data destruction
Every retired asset represents a potential point of exposure if sensitive information remains accessible.
Unlike many cyberattacks that originate outside an organization, improper hardware retirement is entirely preventable. With the right processes, businesses can significantly reduce the likelihood of confidential information leaving their control. The challenge is recognizing that retired hardware deserves the same level of security as active production systems.
Why Improperly Retired Hardware Creates Serious Data Breach Risk
The impact of a data breach from retired hardware extends far beyond the immediate loss of information. Organizations often underestimate the true cost because they focus only on the technical incident, instead of the broader business consequences.
Financial Losses
Responding to a data breach requires significant time and resources. Organizations may incur costs related to forensic investigations, legal services, customer notifications, regulatory reporting, credit monitoring, system remediation, and additional cybersecurity improvements.
What begins as an improperly retired hard drive can quickly become a major financial event.
Regulatory and Compliance Consequences
Many industries require organizations to safeguard sensitive information throughout its entire lifecycle, including disposal.
If retired devices containing confidential data get mishandled, businesses may face compliance investigations, regulatory penalties, or increased scrutiny during future audits. Even if the breach results from third-party handling, organizations may still need to demonstrate that appropriate safeguards were in place before assets left their control.
Damage to Customer Trust
Customers expect organizations to protect their personal information. When sensitive data gets exposed because of improper hardware retirement, rebuilding confidence can be far more difficult than replacing the equipment itself.
Reputation is one of the most valuable assets any business possesses. Once an organization loses trust, customer retention, future business opportunities, and brand perception may all suffer.
Operational Disruption
Responding to a breach often requires IT teams, executives, legal departments, compliance officers, and communications teams to shift their attention away from strategic priorities.
Investigations, reporting requirements, and remediation efforts consume valuable time that could otherwise support business growth and innovation. A preventable retirement mistake can ultimately affect the entire organization.
How Do Data Breaches From Retired Hardware Happen?
Most breaches involving retired IT assets don’t happen because organizations intended to ignore security. Instead, they result from gaps in the retirement process.
Equipment leaves without proper data destruction. Organizations sometimes assume internal formatting or file deletion is enough before selling or recycling equipment. Without verified sanitization using recognized methods, confidential information may remain recoverable.
Assets sit in storage too long. Storage rooms filled with retired servers and laptops often get forgotten over time. These assets may still contain valuable information while receiving little physical security or inventory oversight. The longer equipment stays unmanaged, the greater the chance of loss, theft, or unauthorized access.
Asset tracking stays incomplete. If organizations don’t maintain accurate inventories and a documented chain of custody, they may lose visibility into where retired equipment is or who has handled it. Without proper documentation, it becomes difficult to demonstrate accountability throughout the disposition process.
Organizations use unverified disposal providers. Not every recycler follows the same operational standards. Organizations that choose vendors based solely on convenience or cost may unknowingly expose themselves to greater risk if proper data destruction, documentation, and downstream accountability are missing.
These seemingly small gaps can eventually become the source of a significant security incident.
The Full Cost Stack of a Data Breach From Retired Hardware
When organizations think about the impact of a data breach, they often focus on immediate expenses. But the true cost extends far beyond recovering compromised data or replacing equipment.
A single improperly retired device can trigger financial, operational, legal, and reputational consequences that affect the business for years.
Investigation and Incident Response
The first expense usually begins the moment someone discovers a breach.
Organizations must determine how the incident happened, what information was exposed, which systems were affected, and whether additional devices may also be at risk. This often requires internal IT resources, outside cybersecurity specialists, legal counsel, and compliance teams.
What proper IT asset disposition (ITAD) could have prevented now becomes a costly investigation.
Regulatory Reporting and Compliance
Organizations operating in regulated industries may need to report data breaches to customers, regulators, or other governing bodies.
Failing to demonstrate that retired devices were handled using documented, secure processes can increase regulatory scrutiny and complicate compliance efforts. Maintaining records such as chain of custody documentation, asset inventories, and certificates of data destruction helps organizations show that appropriate safeguards were in place before equipment left their control.
Reputational Damage
Financial losses can often be measured, but damage to reputation is far more difficult to quantify.
Customers expect businesses to protect their personal and confidential information throughout its entire lifecycle, not just while systems are actively in use. When sensitive data gets exposed through improperly retired hardware, organizations may lose customer confidence, delay new business opportunities, and spend years rebuilding trust.
For many organizations, reputational damage ultimately becomes the most expensive consequence of all.
Business Disruption
A breach affects more than just the IT department. Executives, legal teams, compliance officers, communications staff, customer support representatives, and operational leaders may all get pulled into responding to the incident.
Projects get delayed, priorities shift, and valuable time gets redirected toward managing a crisis instead of supporting business growth.
How to Prevent a Retired Hardware Data Breach
The good news: breaches involving retired IT assets are largely preventable. Organizations can significantly reduce risk by implementing a structured IT asset disposition strategy that treats retired hardware with the same level of security as production systems.
Key best practices include:
Maintain complete asset visibility. Document every device scheduled for retirement before it leaves the organization. Maintaining accurate inventories, serial numbers, and asset records helps ensure nothing gets overlooked during the retirement process.
Use secure data destruction. Before reselling, donating, or recycling equipment, organizations should confirm that data-bearing devices undergo appropriate sanitization using recognized industry guidance. Organizations should always verify and document secure data destruction before assets leave their control.
Establish chain of custody. Document every transfer from collection through final disposition. Maintaining an uninterrupted chain of custody provides accountability throughout transportation, processing, and asset retirement while supporting future audits and compliance requirements.
Partner with qualified ITAD providers. Selecting an experienced IT asset disposition provider helps organizations combine secure data handling, documentation, value recovery, and responsible recycling into one structured process. Rather than treating retirement as a disposal task, organizations can manage it as a continuation of their overall cybersecurity and lifecycle management strategy.
Common Mistakes That Increase Retired Hardware Data Breach Risk
Even organizations with mature cybersecurity programs can overlook risks during hardware retirement.
Assuming deleting files is enough. Deleting files or performing a quick format doesn’t necessarily remove sensitive information from storage devices. Organizations should ensure retired media undergoes appropriate sanitization before leaving their control.
Leaving retired equipment in storage. Old servers and laptops stored indefinitely remain both a security risk and a financial burden. Delaying retirement also reduces potential resale value while increasing opportunities for theft or unauthorized access.
Choosing disposal providers based only on cost. The lowest-cost option isn’t always the safest. Organizations should evaluate providers based on documented processes, secure handling procedures, chain of custody, and accountability, not simply pricing.
Failing to document the process. Without documentation, organizations may struggle to demonstrate how they handled retired assets or verify that someone securely destroyed sensitive information. Maintaining complete records is just as important as performing the data destruction itself.
Expert Insight: Stopping a Retired Hardware Data Breach
Strong cybersecurity doesn’t end at the firewall. Every device eventually reaches the end of its lifecycle, and the retirement process deserves the same level of planning and oversight as deployment and daily operations.
Organizations that build IT asset disposition into their cybersecurity strategy reduce risk by keeping retired hardware protected until its final disposition is complete. Secure data destruction, documented chain of custody, responsible recycling, and comprehensive reporting work together to close one of the most commonly overlooked gaps in enterprise security.
The safest device isn’t the one that’s been unplugged, it’s the one that’s been securely retired.
Frequently Asked Questions
While many organizations focus on cyberattacks targeting active systems, a data breach from retired hardware remains a recognized source of exposure when sensitive information isn’t securely removed before disposal.
Organizations remain responsible for selecting qualified ITAD providers and maintaining appropriate oversight of their asset disposition process. Documented procedures and chain of custody help strengthen accountability.
The safest approach combines secure data destruction, documented asset tracking, verified chain of custody, and responsible IT asset disposition through an experienced provider.
Documentation provides evidence that retired assets were handled securely, supports audit readiness, and helps organizations demonstrate compliance with internal policies and regulatory requirements.
Eliminate Retired Hardware Risks Before They Become a Data Breach
Your cybersecurity strategy shouldn’t end when hardware leaves the data center or office. Every retired server, laptop, storage device, and network appliance deserves the same level of protection as the systems still running your business.
Talk to Silverback Communications about building a secure IT asset disposition strategy that protects sensitive data, strengthens compliance, and reduces the risk of a data breach from retired hardware throughout your entire technology lifecycle.
Want to identify potential gaps in your current retirement process? Download our Retired Asset Risk Audit Checklist to evaluate your IT asset disposition practices and strengthen your organization’s security before your next hardware refresh.
Keep reading
IT Equipment Lease Return: Avoiding Penalties and Data Risk
Plan your IT equipment lease return to avoid penalties and protect data with a clear, step-by-step process.
SSD Data Destruction Guide: Why SSDs Are Different
Why wiping fails on flash drives, and which methods actually remove your data from SSDs.
How to Choose an ITAD Vendor
The certifications, data security checks and red flags that separate a safe ITAD partner from a liability.